open source · windows & linux
Know what listens. Know what is exposed.
SocketScope is a local, read-only endpoint inspector. It connects TCP and UDP endpoints with process, service, container, interface and firewall evidence without presenting local indicators as proof of Internet reachability.
v1.0.0C#

purpose
An endpoint is more than a port number.
SocketScope shows which process listens on which address, which service or container may be behind it and which local firewall rules are relevant candidates.
The tool is deliberately read-only: it does not scan other systems, does not change any firewall and does not claim that local evidence alone proves actual reachability from the Internet.
features
Analyze read-only. Back it up cleanly.
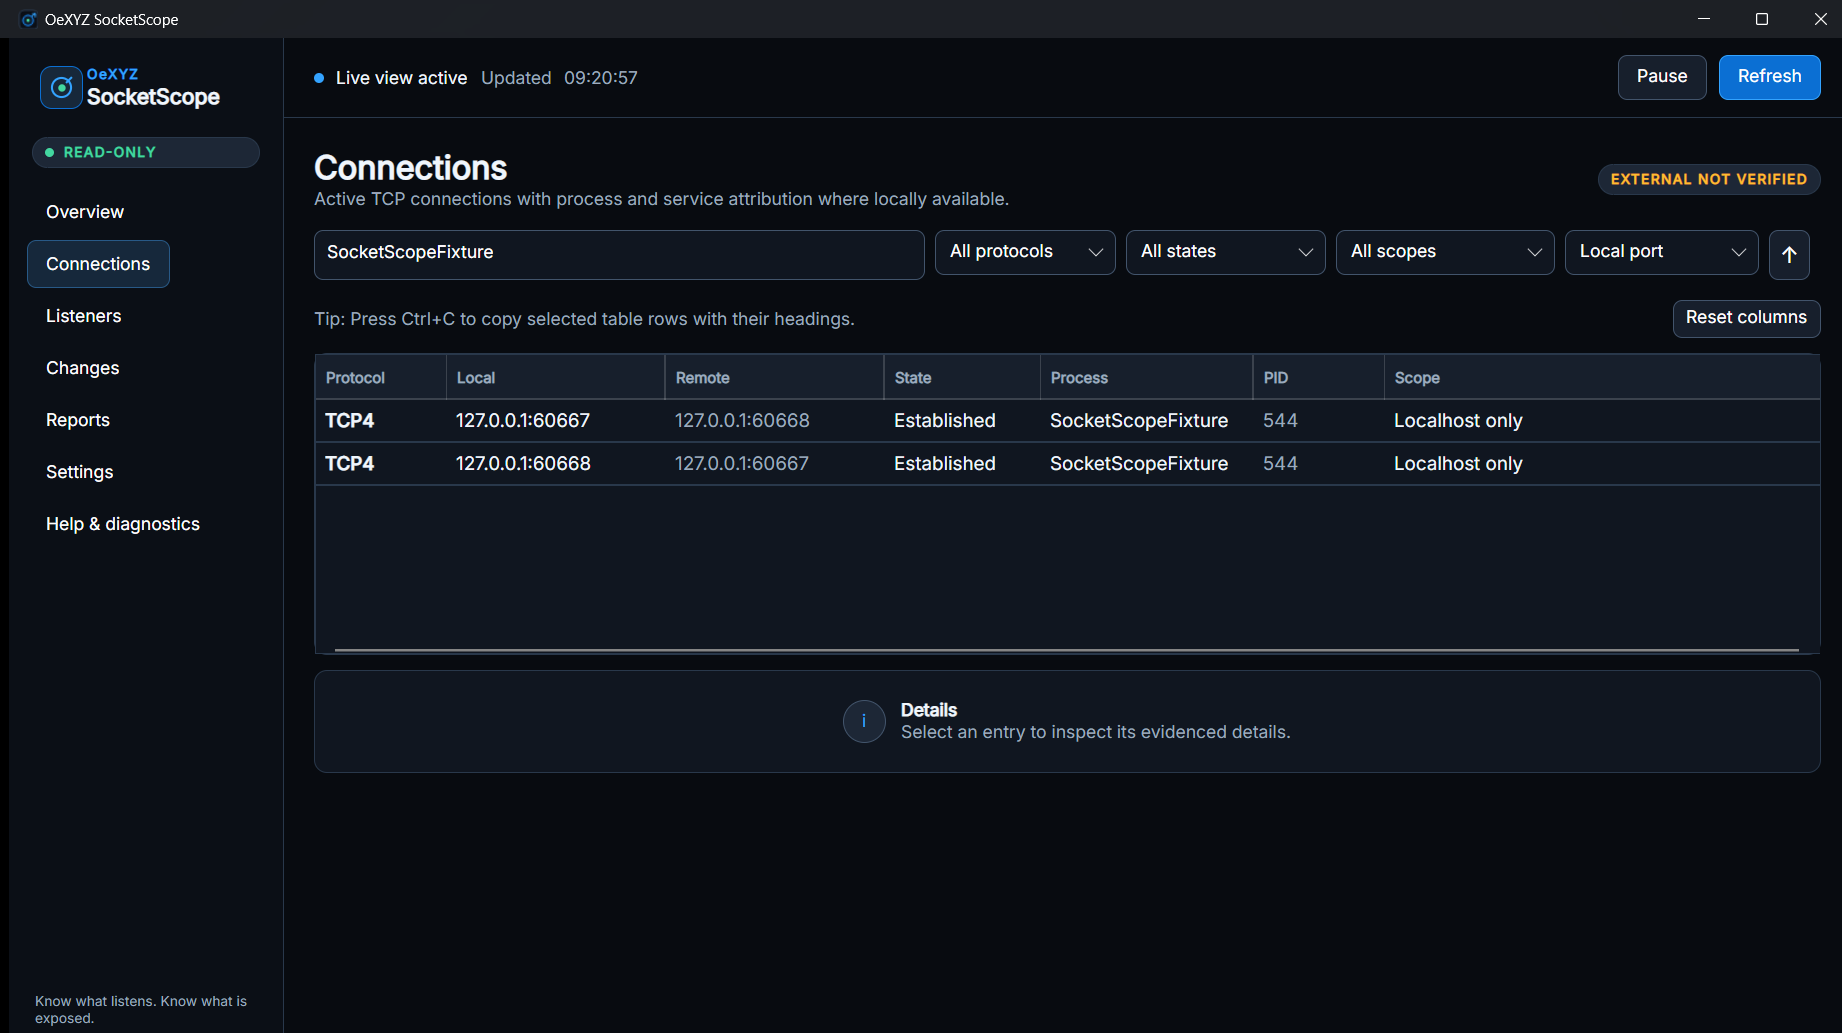
TCP & UDP inventory
Live view for IPv4 and IPv6 with listeners, active connections, state, and local and remote endpoints.
Owner Attribution
Best-effort attribution to process, PID, path, Windows service, systemd unit, cgroup or container.
Binding classification
Loopback, wildcard and specific interfaces are shown separately so that binding scope and context stay clear.
Firewall evidence
Matching local rules are shown as candidates, as traceable evidence and not as a security guarantee.
Snapshots & comparison
States can be captured and compared locally to spot new, removed or changed endpoints faster.
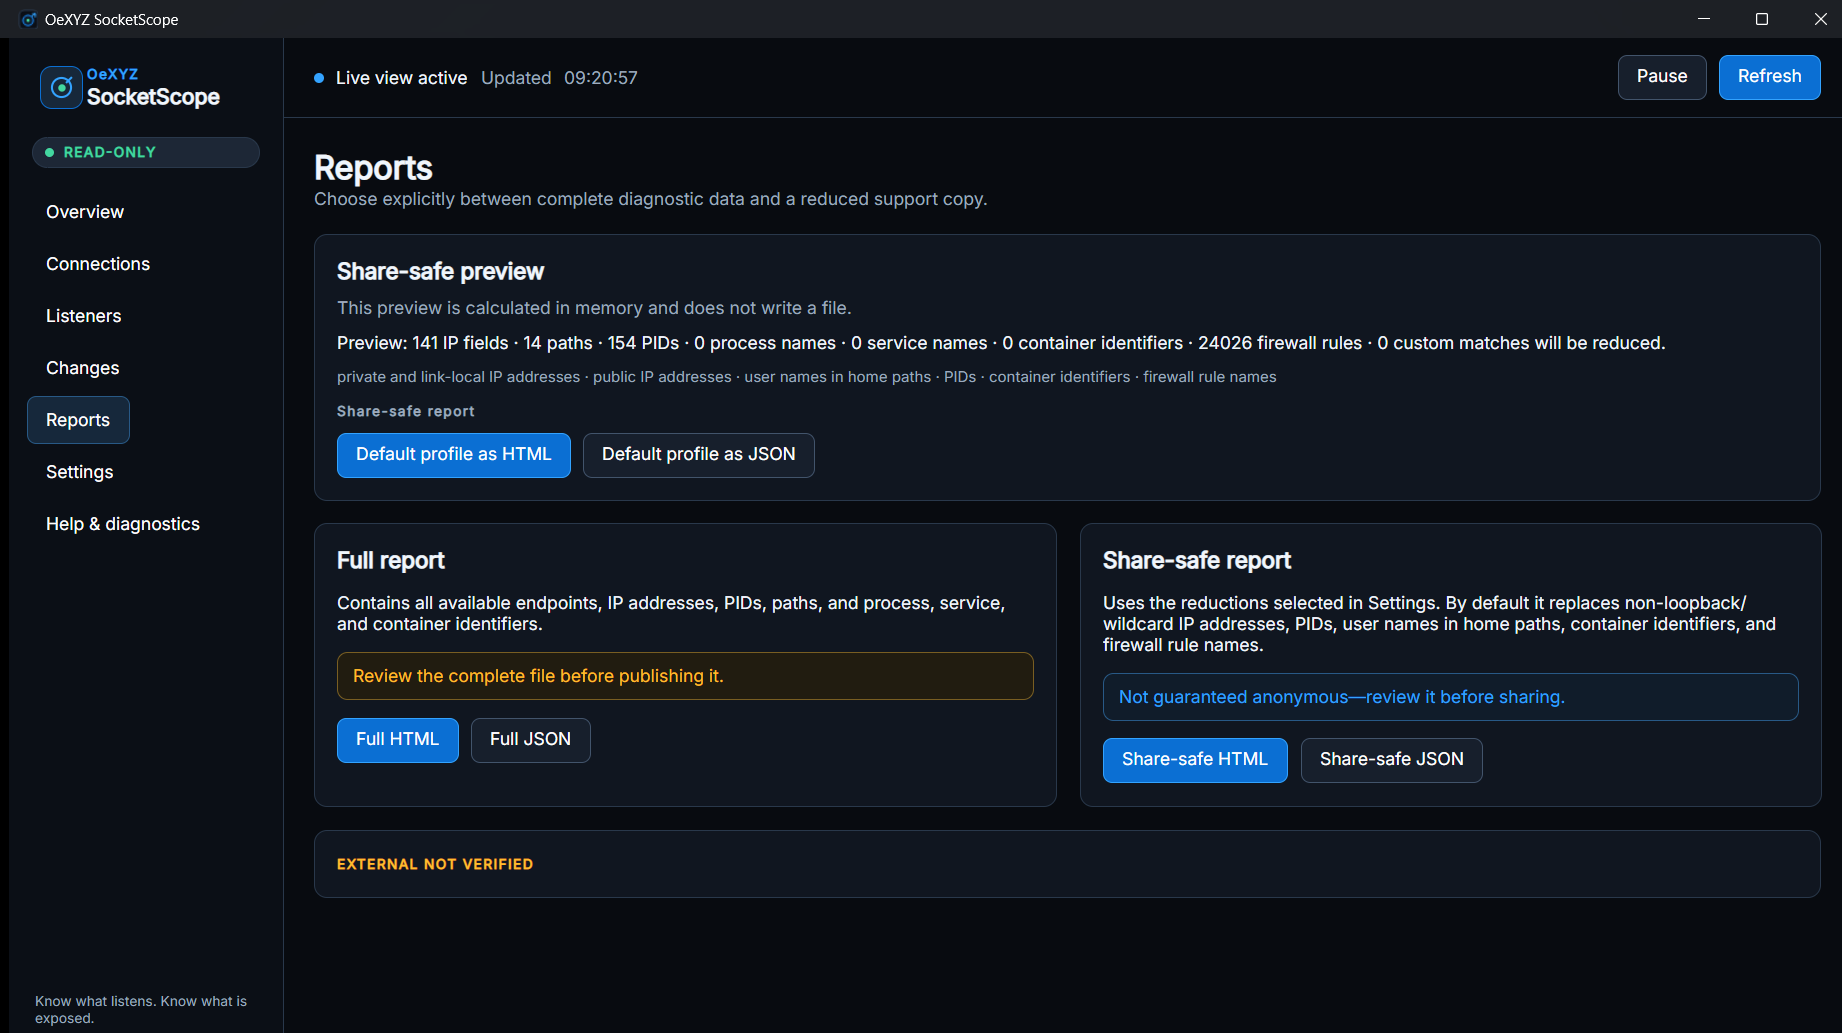
Share-safe Reports
Full or sanitized HTML and JSON reports support diagnosis and sharing without unnecessary local details.
operating model
Local. Read-only. No account.
- Platforms
- Windows · Linux
- Architectures
- x64 · ARM64
- Permissions
- Standard user · no service
- Data
- Local · no telemetry
- Tests
- 216 automated tests
- License
- MIT
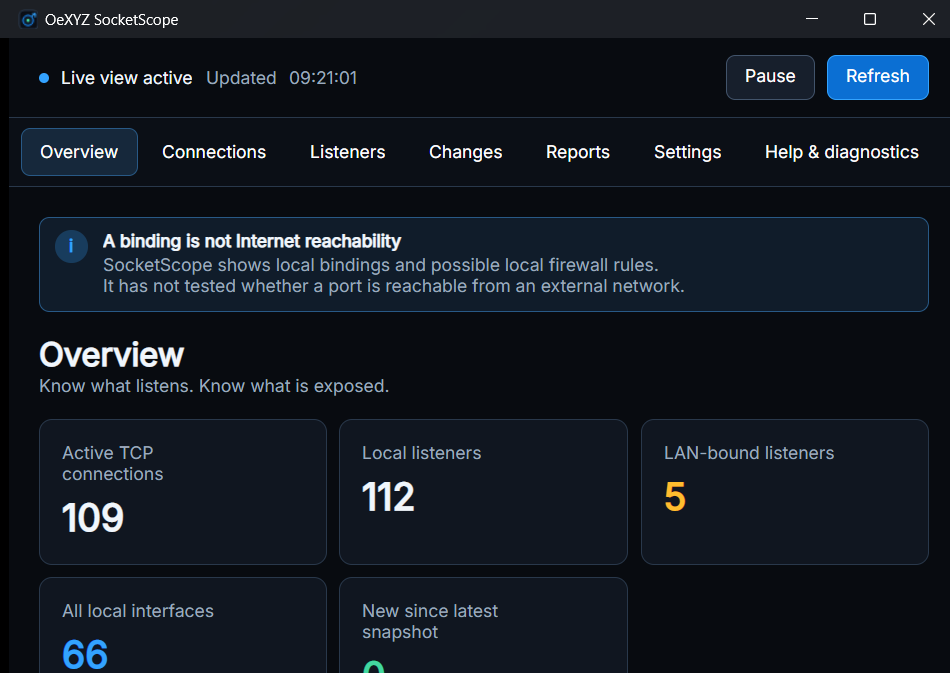
Local evidence is not an external reachability test.
SocketScope shows what a machine can observe locally. NAT, upstream firewalls, routers, provider filtering and other network paths are outside that evidence. Therefore, “reachable from the Internet” remains explicitly unconfirmed until a separate external test has taken place.
roadmap
The analysis is done. Changes stay controlled.
The roadmap follows the public repository. Planned features are not yet part of the current release.
Local endpoint inspector
Windows and Linux inventory, attribution, binding and firewall evidence, snapshots, comparisons and sanitized reports.
Deeper network evidence
Stronger container and NAT attribution, optional external checks, remote hosts, notifications and native packages.
Privileged actions
Process, service, firewall or container changes come into question only with their own threat model, preview, explanation and explicit confirmation.
$ git clone https://github.com/Oexyz/SocketScope
Source code, documentation, platform notes, tests and releases are publicly available on GitHub.